Joomla vs WordPress (2026): Choosing a CMS for Your Website
In 2026, the choice between Joomla and WordPress remains central for anyone planning a new website or reconsidering their current platform.
Home of inspirations for Joomla users, developers, designers, and website owners.
Joomla matters in a web developer’s life. With its clean structure, flexible architecture, and user-friendly administration interface, Joomla makes it possible to build and manage professional websites efficiently — even for users who are just starting their journey.
Thanks to the large open-source community and thousands of extensions available, Joomla continues to be one of the most powerful and scalable CMS platforms available today.
JoomlaForever was created to provide an easy, practical, and inspiring introduction to Joomla. Our goal is not to overwhelm you with technical theory, but instead guide you toward building, improving, and maintaining Joomla websites in a real-world environment.

Joomla!® — A powerful open-source CMS with advanced features and easy administration.
Learn the fundamentals of Joomla, its ecosystem, architecture, and best practices.
Step-by-step tutorials created by JoomlaForever and the Joomla community.
Discover useful techniques, workflows, and optimizations for Joomla websites.
Independent reviews of Joomla extensions, tools, hosting solutions, and services.
Join discussions, connect with other Joomla users, and share knowledge.
Access curated Joomla resources, official documentation, and recommended tools.
Whether you are building your first Joomla website or managing advanced production environments, JoomlaForever is here to guide and inspire you.
In 2026, the choice between Joomla and WordPress remains central for anyone planning a new website or reconsidering their current platform.
Joomla stores using J2Store 6.0.0 through 6.6.5 should address CVE-2026-102803, a voucher and coupon race condition that can allow an authenticated customer to apply one benefit to more than one order. Update to a non-affected release, review recent discounted orders, and monitor checkout activity while...
jDownloads 4.1.8 is a security update for Joomla sites that addresses five vulnerabilities affecting versions 1.0.0 through 4.1.7, including a critical remote code execution flaw requiring frontend upload permission. Site owners should update to 4.1.8 or later promptly, restrict frontend uploads until...
AcyMailing 11.1.2 addresses seven published CVEs affecting releases through 11.1.1, including two High-rated CVSS 4.0 issues scored 8.8 by the Joomla CNA. Joomla administrators should update promptly, verify the installed version, and review subscriber, campaign and access-controlled content...
Hard-coded http://localhost URLs can survive a Joomla migration and send visitors to the wrong place, even when the new site otherwise appears to work. This practical Joomla tutorial explains how to prevent new incorrect links in JCE, clean existing content carefully, and validate the result...
Joomla’s accessibility checker can help you locate accessibility problems while you are editing content, but the documented guidance is clear that it identifies issues rather than correcting them for you. The preserved research also notes that the reported symptom may involve empty links, missing text...
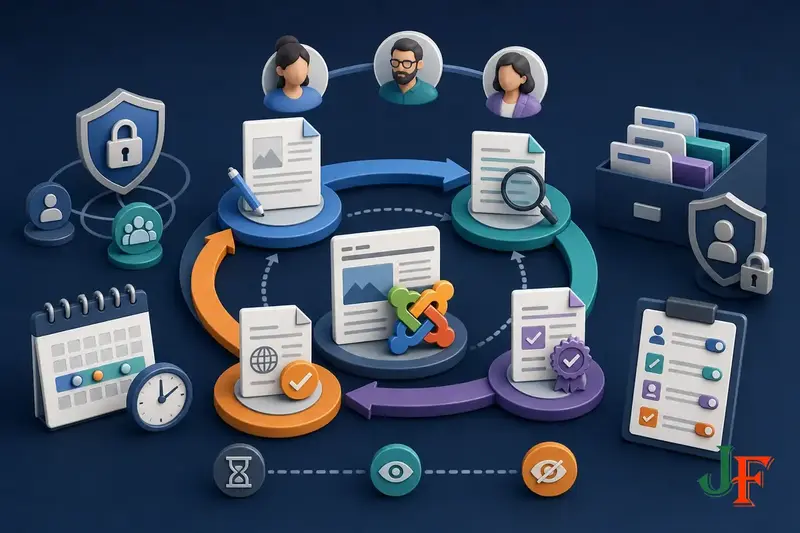
A well-designed Joomla publishing workflow gives a small editorial team a repeatable path from first draft to reviewed, approved, scheduled, and published content. Instead of allowing every contributor to publish, the team can separate writing, editorial review, approval, and publication...
The Joomla error Class "JPlugin" not found can take down part or all of a site when older extension code, an incomplete change, or a compatibility mismatch tries to load a class that is unavailable. This practical Joomla tutorial explains how to protect the site first, identify the extension or...
Joomla’s “File Checksum Failed” message means an update or file-integrity check found that a file does not match the expected data. It is not a documented CVE-based vulnerability, but it should be handled carefully: a failed check can result from an interrupted download or configuration problem, and it...
Joomla developer-impersonation scams rely on trust, urgency and requests for access rather than a newly disclosed Joomla software flaw. Learn how to verify unexpected contacts, control third-party access and respond quickly if credentials or site access may have been exposed.
Joomla sites running YOOtheme Pro 5.0.0 through 5.0.52 should update to version 5.0.53 or later without delay. CVE-2026-102785 is an unauthenticated remote code execution vulnerability in the extension’s public image transformation handler, with an official CVSS 4.0 score of 10.0 CRITICAL.
CVE-2026-102786 is a critical vulnerability in PHP, not Joomla core, but Joomla sites may be exposed when their server runs an affected PHP release. Administrators should identify the runtime version, arrange a server-level update where needed, and validate the site after the upgrade.
A hosting-side WAF change can sometimes prevent legitimate Joomla administrator requests from completing, leaving article, configuration or form saves unable to finish as expected. This is a configuration and compatibility troubleshooting issue, not a confirmed Joomla or cPanel vulnerability, and...
This Joomla tutorial explains a practical local-development workflow with ServerMaster for developers who prefer not to assemble a MAMP stack or container configuration for every project. It also sets clear boundaries: a local runtime is for trusted development work and is not a substitute for...
When every Joomla article appears to open the same page, the documented behavior points first to menu-item routing and, on sites using SP Page Builder, to the global article-details layout setting. The records here do not confirm a core Joomla defect on the affected site; they only show that a...
